Timeline
Every post and feed across this instance
-
New cPanel Flaw Lets a Hosting Account Run Code as Root, Take Full Server Control
New cPanel Flaw Lets a Hosting Account Run Code as Root, Take Full Server Control
A flaw in cPanel's CalDAV and CardDAV service lets anyone with a cPanel hosting account run code as root and take "full control of the server," the company said on September 22. A second bug in the WP ... Read more
Published Date: Sep 23, 2026 (4 days, 22 hours ago)Vulnerabilities has been mentioned in this article.
-
Two Git ignore files nobody told me about
Article URL: https://mihai.dinculescu.dev/posts/two-git-ignore-files-nobody-told-me-about/
Comments URL: https://news.ycombinator.com/item?id=49814432
Points: 95
# Comments: 65
-
Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
A use-after-free in the Linux kernel's AF_UNIX socket subsystem can be used to escape a container and gain root on the host, security firm DepthFirst said in research published September 22. The flaw, ... Read more
Published Date: Sep 23, 2026 (4 days, 23 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-80521 -
Chrome 154 verhelpt in totaal 108 kwetsbaarheden
Chrome 154 verhelpt in totaal 108 kwetsbaarheden
Google heeft een nieuwe Chrome versie beschikbaar gesteld waarin 108 kwetsbaarheden zijn verholpen. Van de 108 kwetsbaarheden worden 11 aangemerkt als "critical", 25 als "high", 47 als "medium" en 25 ... Read more
Published Date: Sep 23, 2026 (4 days, 23 hours ago)Vulnerabilities has been mentioned in this article.
-
CISA en NCSC waarschuwen voor kwetsbaarheid in Arista VeloCloud
CISA en NCSC waarschuwen voor kwetsbaarheid in Arista VeloCloud
Het Amerikaanse Cybersecurity and Infrastructure Security Agency (CISA) en het Nederlandse Nationaal Cyber Security Centrum (NCSC) waarschuwen voor een actief aangevallen kwetsbaarheid in Arista VeloC ... Read more
Published Date: Sep 23, 2026 (5 days, 1 hour ago)Vulnerabilities has been mentioned in this article.
CVE-2026-93952 -
Using shallow-Git tarballs for CI
Article URL: https://people.kernel.org/monsieuricon/using-shallow-git-tarballs-for-ci
Comments URL: https://news.ycombinator.com/item?id=49813302
Points: 2
# Comments: 0
-
F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers
F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers
Attackers are exploiting a critical flaw in F5 BIG-IP Access Policy Manager (APM) that lets them run code on a BIG-IP system without logging in, F5 says. The flaw, CVE-2026-94127, affects only systems ... Read more
Published Date: Sep 23, 2026 (5 days ago)Vulnerabilities has been mentioned in this article.
CVE-2026-94127 CVE-2025-53521 -
Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware
Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware
A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The attacks, detected on ... Read more
Published Date: Sep 23, 2026 (4 days, 19 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-87491 CVE-2026-85880 CVE-2026-85046 -
NCSC waarschuwt voor actief misbruikt zerodaylek in F5 BIG-IP
NCSC waarschuwt voor actief misbruikt zerodaylek in F5 BIG-IP
Het Nationaal Cyber Security Centrum (NCSC) waarschuwt organisaties voor een ernstige kwetsbaarheid in F5 BIG-IP Access Policy Manager (APM) die monenteel actief wordt misbruikt. F5 heeft beveiligings ... Read more
Published Date: Sep 23, 2026 (4 days, 1 hour ago)Vulnerabilities has been mentioned in this article.
CVE-2026-94127 -
Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input
Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input
A new security vulnerability in Next.js could allow attackers to run code on a server via ImageResponse, the feature that generates Open Graph and other social preview images, Vercel said. The risk ap ... Read more
Published Date: Sep 23, 2026 (3 days, 14 hours ago)Vulnerabilities has been mentioned in this article.
-
ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
The cyber extortion group known as ShinyHunters on Tuesday claimed it had breached the U.S. Federal Bureau of Investigation and stolen data belonging to current and former employees at the agency. "We ... Read more
Published Date: Sep 23, 2026 (3 days, 11 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-35273 -
It's Donald Trump Versus MAGA on Data Centers | The president has doubled down on data centers and AI. His base is running in the opposite direction.
submitted by Mustachius_Grumpius to technology
68 points | 15 comments
https://www.wired.com/story/donald-trump-versus-maga-on-data-centers -
Grammarly will send unhinged messages to all your users if you try to cancel
Article URL: https://www.reddit.com/r/sysadmin/comments/1wjdpgx/psa_grammarly_will_send_unhinged_messages_to_all/
Comments URL: https://news.ycombinator.com/item?id=49811484
Points: 390
# Comments: 104
-
Advertising Is Content: An Absurd Ikea Mod For Skyrim
A theme going on many years here at Techdirt has been the idea that separating content and advertising, as was the traditional model, makes far less sense in the modern era. Audiences are no longer captive in the way they used to be, with many ways to skip advertising. Entertainment vectors are far more plentiful […] -
CISA adds Five Vulnerabilities to Exploitable Catalog
CISA adds Five Vulnerabilities to Exploitable Catalog
CISA’s Known Exploited Vulnerabilities (KEV) Catalog continues to highlight a familiar pattern: vulnerabilities affecting network infrastructure, security appliances and management platforms are beco ... Read more
Published Date: Sep 23, 2026 (3 days, 10 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-93616 CVE-2026-85102 CVE-2026-16812 CVE-2026-7273 CVE-2026-9501 -
How the Meta Settlement Silences Youth Activism
Since its integration into our digital world, social media has played a pivotal role in youth organizing and social mobilization. Yet, people’s access to these platforms is increasingly coming under threat from courts and legislatures under the guise of protecting young people online—presenting a significant hindrance to youth organizing. In a major recent example, Meta settled in a lawsuit with 52 states and territories regarding the use of Instagram and Facebook by young people. The settlement will require Meta, and […] -
WordPress Board Resignations
-
Git-bug, project bug tracker tool using Git objects as storage, releases v0.11.0
Article URL: https://github.com/git-bug/git-bug/releases/tag/v0.11.0
Comments URL: https://news.ycombinator.com/item?id=49808127
Points: 2
# Comments: 2
-
[object Object]
[object Object]
BackgroundDarkMe, a Visual Basic 6 (VB6) spy trojan and remote access tool became well known in February 2024 for its use of zero days to deliver malware. But this malware family was first observed in ... Read more
Published Date: Sep 22, 2026 (2 days, 20 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2024-21412 CVE-2023-38831 CVE-2017-18362 -
Appeals Court Rejects ICE Detention Policy, Comparing It To WWII Japanese Internment
Ever since Trump’s return to office, almost every federal law enforcement agency has been ordered to treat illegal immigration as their first priority. This is why the administration is gutting FEMA to direct more dollars to detention and removal efforts. And that’s why ICE is now the administration’s largest law enforcement budget line item. To […] -
Show HN: Riftri – copy-on-write Git worktrees for running agents in parallel
Article URL: https://twitter.com/KinfishT/status/2102093551601684897
Comments URL: https://news.ycombinator.com/item?id=49807251
Points: 5
# Comments: 2
-
ShinyHunters claims FBI hack: 'This is NOT financially motivated'
-
‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees
-
Larry Page, Sergey Brin, and Peter Thiel All Fled California’s Billionaire Tax. Nvidia’s CEO Isn’t Going Anywhere. Even With an $8 Billion Bill Coming His Way
submitted by Mustachius_Grumpius to technology
44 points | 5 comments
https://finance.yahoo.com/economy/policy/articles/larry-page-sergey-brin-peter-182255068.html?guccounter=1&%3Bguce_referrer=aHR0cHM6Ly93d3cuZ29vZ2xlLmNvbS8&%3Bguce_referrer_sig=AQAAAHx6dPfBRIuZlh05I44ac7MoCt2V79RpqW0ljwiUyGEvuWLDImtMnZ8nTaoQmpcTmk7LTMcRJ0fmTvi-q1maI-a-DB37BgOjMCgdNJddzCA7kvQ0Ul7gNvWNCNhubYXS1klmEGlbyA5vPH05Zer8-3BnnTrQRt9YXi4NwKnkEwhS -
Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks
Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks
Attackers exploited a previously unknown flaw in Check Point's Security Management Server in a handful of targeted attacks on July 23, the company said. The flaw, CVE-2026-93616, allows an attacker wh ... Read more
Published Date: Sep 22, 2026 (2 days, 19 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-93616 CVE-2026-91843 CVE-2026-85103 CVE-2026-85102 -
Elon Said Fighting CSAM Was “Priority #1.” A NY Times Reporter With A Script Found 75 Known Images.
When Elon first took over Twitter with grand plans to “bring back free speech,” I tried to help him run through the standard content moderation learning curve that basically every site created by a clueless tech bro runs through. They all start with “we’re the free speech site, we allow everything!” and very quickly someone […] -
WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers
WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers
WordPress has fixed a critical flaw in its core software that lets an attacker with no account make a site load a PHP file from outside its theme folders. On some servers, that can go further, allowin ... Read more
Published Date: Sep 22, 2026 (2 days, 18 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-87902 -
Daily Deal: Soundfreaq Sound Spot II Bluetooth Speaker
The Soundfreaq Sound Spot II combines wireless audio performance, ambient lighting, and relaxing sound features in a compact design built for modern lifestyles. Featuring a Bamboo and White finish with eco-friendly materials, this Bluetooth speaker complements bedrooms, offices, living rooms, and personal spaces while delivering both style and functionality. Engineered with a custom-designed audio driver, […] -
Show HN: Task and test management as YAML in your Git repo (VS Code)
Article URL: https://github.com/gitoza-io/gitoza-lite
Comments URL: https://news.ycombinator.com/item?id=49804960
Points: 1
# Comments: 0
-
Custom email aliasing – throw-away emails using a custom domain
submitted by RougeEric to technology
21 points | 4 comments
https://eric-lowry.com/blog/2026-09-22Hi there!
I’ve been eyeing email aliasing services like Firefox Relay or Proton’s Hide-my-email feature for a while, but I’m cheap!
Well, that and I tend to like doing things myself whenever possible.So after a bit of investigating I found out that using Cloudflare and a custom domain name, you can essentially get infinite free email aliases that get redirected to an existing email address (Gmail in my case, but I’m working on moving over to Proton at the moment).
One thing lead to another, and I ended up coding a Firefox extension to automatically inject aliases into email input fields using a custom domain name.
Because I find this whole setup cool, and am fairly certain that other people could benefit from it, I wrote up a full guide on my blog. I’m no Cloudflare or DNS expert, so feel free to point out any mistakes or make suggestions here or in my post’s comments ;).
Note: Yes, I know that using a custom domain reduced the privacy benefits.
-
Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials
Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials
A critical vulnerability in Bifrost, an open-source AI gateway that routes requests to more than 20 LLM providers, allows an unauthenticated attacker to run arbitrary commands on the gateway server wi ... Read more
Published Date: Sep 22, 2026 (2 days, 15 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-90898 CVE-2026-86242 CVE-2026-55245 CVE-2026-42271 -
WordPress: Unauthenticated path traversal leading to conditional RCE
Article URL: https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-7hp8-65ch-5whp
Comments URL: https://news.ycombinator.com/item?id=49803959
Points: 239
# Comments: 132
-
ICE Officer Who Dodged Extradition To Minnesota Arrested By MN Cops One Day Before His *Federal* Criminal Court Appearance
I love everything about this. I love the way this ICE officer was picked up. I love the fact that his lawyer claims an arrest is the same thing as “surrendering.” And I especially love the fact that this officer is in state custody only a day prior to scheduled court appearance to face federal […] -
Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates
Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates
A zero-day proof-of-concept tool that stops Microsoft Defender from installing platform and signature updates by filling all available disk space was published on GitHub on September 19. The tool, cal ... Read more
Published Date: Sep 22, 2026 (2 days, 15 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-45498 -
iPhone users are flooding social media with complaints — Apple’s latest iOS move is adding persistent ‘ads’ that can’t be dismissed to users’ devices
submitted by XLE to technology
67 points | 7 comments
https://www.techradar.com/phones/iphone/i-wish-apple-would-just-stop-that-crap-apple-has-added-persistent-ads-to-ios-and-its-driving-users-crazyInfuriatingly for iOS users, the only way to disable these promos is to either let them expire — which in many cases could take weeks or even months, leaving a persistent notification badge on the Settings app in the meantime — or pay for the service being offered.
-
iPhone users are flooding social media with complaints — Apple’s latest iOS move is adding persistent ‘ads’ that can’t be dismissed to users’ devices
submitted by XLE to technology
40 points | 7 comments
https://www.techradar.com/phones/iphone/i-wish-apple-would-just-stop-that-crap-apple-has-added-persistent-ads-to-ios-and-its-driving-users-crazyInfuriatingly for iOS users, the only way to disable these promos is to either let them expire — which in many cases could take weeks or even months, leaving a persistent notification badge on the Settings app in the meantime — or pay for the service being offered.
-
Binomial Coefficient Coincidences
Article URL: https://johncarlosbaez.wordpress.com/2026/09/20/binomial-coefficient-coincidences/
Comments URL: https://news.ycombinator.com/item?id=49803132
Points: 2
# Comments: 0
-
D-Link waarschuwt voor kritieke kwetsbaarheid in wifi-router
D-Link waarschuwt voor kritieke kwetsbaarheid in wifi-router
D-Link waarschuwt voor een kritieke kwetsbaarheid in de DIR-822A wifi-routers waar op dit moment nog geen patch voor beschikbaar is. De kwetsbaarheid (CVE-2026-86296) betreft een stackoverflow in het ... Read more
Published Date: Sep 22, 2026 (2 days, 5 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-86510 CVE-2026-86296 -
The Middle Powers Are Now the “Free World”
-
MikroTrick: technical analysis, disclosure process, and the use of LLM agents
MikroTrick: technical analysis, disclosure process, and the use of LLM agents
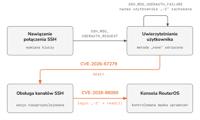
Introduction On 3 September 2026, MikroTik released patches almost simultaneously for several maintained RouterOS branches: 7.25beta3, 7.24.2, 7.23.4, and 6.49.21, and recommended installing a patched ... Read more
Published Date: Sep 22, 2026 (2 days, 2 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-86060 CVE-2026-67279 CVE-2026-67277 CVE-2026-67276 -
Show HN: Drop – A rootless Linux sandbox with gVisor support
I created Drop because I always felt uneasy installing and running third-party programs using my main user account. A single compromised dependency means a full compromise of the system. What is even worse, because I ship software from my computer, a single compromised dependency can lead to compromise of all the users of my software.
Containers and VMs are one solution, but for local work, they are often detrimental to productivity. It takes effort to configure a machine with all the tools and configs needed for productive work, but a container or a VM will be stripped of all these tools. This is great for production deployments, where the aim is a reproducible system with minimal dependencies, but can get in the way of productive local work.
Drop is language independent, but the workflow is inspired by Python's virtualenv. With virtualenv the environment isolation is only a convention that relies on installed dependencies being good citizens. With Drop the isolation is enforced.
Each Drop environment gets its own writable and easily disposable home dir, with only selected config files and dirs from the original home mounted, mostly read-only.
Drop uses Linux namespaces for isolation (user, mount, network, PID, IPC, cgroup), doesn't require root and, as an option, uses gVisor user-space kernel, which adds protection against exploiting host kernel vulnerabilities to escape the sandbox.
I don't want to make the introductory post too lengthy, but I'm here to answer any questions and give any additional technical details.
Note: This is my 3rd submission of the project, the first two did not draw attention. Since then I have added support for gVisor and created a project website to better explain the concept and organize documentation.
Comments URL: https://news.ycombinator.com/item?id=49801329
Points: 193
# Comments: 63
-
Don’t be fooled by this summer of AI hype
submitted by halm to technology
63 points | 7 comments
https://www.technologyreview.com/2026/09/22/1144867/dont-be-fooled-summer-ai-hype/By Emily Bender and Timnit Gebru, timely and thoughful as ever:
Claims of incipient, dangerous superintelligence are not based in good scientific or engineering practice. Rather, they are narratives based in ideologies of transhumanism, eugenics, and wishful thinking about imagined future digital humans.
[…]
the illusion of speed and urgency promulgated by the tech companies is also a ploy to misdirect both policymakers and the public. Unfortunately, it sometimes works, such as with Senator Bernie Sanders’s well-meaning but ultimately misguided proposed legislation to prevent the development of “artificial superintelligence.”
Describing them as “superintelligence” or “rogue models” ascribes agency to products rather than to the companies building them. This framing markets these companies’ products as “superhuman” and, at the same time, helps the companies evade accountability for their actions.
-
Show HN: EnvSeal-CLI – Git for Secrets, Offline Git-Native Secret Manager
Article URL: https://github.com/viswajith275/EnvSeal-CLI
Comments URL: https://news.ycombinator.com/item?id=49800898
Points: 4
# Comments: 6
-
Show HN: JevBench, a reproducible benchmark for typed decision models
Hi HN! I built JevBench because Jev kicks ass, and the world deserves to know how the serious open source and fake lookalike projects really perform in comparison.
Jev-class models return bounded choices and probabilities instead of text, and are disruptively faster and cheaper than LLMs, while being similarly intelligent on the text input they operate on.
JevBench allows looking at accuracy, latency and price all at once, in a weighted way - you can even configure the weighting.
A full run asks 534 English decisions. The v1.3 score combines chance-corrected Intelligence, Calibration, Speed and Cost.
Leaderboard right now:
MIT harness, public items, frozen artifacts, scoring code and public per-task outcomes:#1 - Jev 74.4 #2 - SemIf 73.1 #3 - djev 73.0 #4 - Winnow-12B Q8 71.2 #5 reflex 4B 70.3.https://github.com/fstandhartinger/jevbench
Two no-signup demos:
https://who-is-right.app.mintapis.com
https://is-it-ai-slop.app.mintapis.com
Limitations: English-only; latency from one German server; local/demo latency gets a disclosed ×2 adjustment (+150 ms on my servers) which is an informed assumption; held-out prompts still reach evaluated services; ~1-point gaps can be noise.
Wdyt?
Comments URL: https://news.ycombinator.com/item?id=49800574
Points: 153
# Comments: 39
-
New CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based Setups
New CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based Setups
Attackers are exploiting a new flaw in on-premises VeloCloud Orchestrator (VCO), the server that manages the Edge devices in a VeloCloud SD-WAN, Arista said on September 22. The flaw, tracked as CVE-2 ... Read more
Published Date: Sep 22, 2026 (2 days, 4 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-93952 CVE-2026-16812 -
America Last: Trump FCC Rubber Stamps Major Saudi, Chinese Investment In Paramount Merger
There was a four year span where Trump FCC boss Brendan Carr simply couldn’t stop hyperventilating about the fact that TikTok’s parent company, ByteDance, was Chinese. Carr would appear on cable news pretty much every week to endlessly rant about the potential propaganda, privacy, and NatSec impact of what was (at best) fairly murky Chinese […] -
What to Expect in the AI Era
Article URL: https://igorpak.wordpress.com/2026/09/15/what-to-expect-in-the-ai-era/
Comments URL: https://news.ycombinator.com/item?id=49800056
Points: 1
# Comments: 0
-
Show HN: Nimblegate – Git push guardrails for AI agents
Article URL: https://github.com/nimblegate/nimblegate
Comments URL: https://news.ycombinator.com/item?id=49799938
Points: 4
# Comments: 1
-
New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory
New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory
A new flaw in the Linux kernel's KVM virtualization code for ARM64 processors can leave a freed piece of host memory exposed to a guest virtual machine on hosts with nested virtualization enabled. The ... Read more
Published Date: Sep 22, 2026 (1 day, 22 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-89775 -
SharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCE
SharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCE
A SharePoint Server vulnerability that Microsoft initially classified as a spoofing flaw with a CVSS score of 6.5 actually enables authenticated remote code execution, according to full technical deta ... Read more
Published Date: Sep 22, 2026 (1 day, 21 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-65660 CVE-2026-55040