Timeline
Every post and feed across this instance
-
Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far
Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far
An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on October 13. Ivanti has released fixes for ... Read more
Published Date: Oct 13, 2026 (15 hours, 28 minutes ago)Vulnerabilities has been mentioned in this article.
CVE-2026-109412 CVE-2026-106042 CVE-2026-104935 -
💬 @rmdes — PR #960 : build: official container image with release and manual preview channels
Commentaire de pull request · PR #960 build: official container image with release and manual preview channels · @rmdes
I wanted to test the workflow, so I ran
docker-previewby hand frommainto confirm it works: it did (run 38438316241), and pushedpreview-31andpreview-31-7563895. So theindiekitpackage exists now; it just needs switching to public in its package settings. (docker-releasecan’t buildv1.0.0-beta.31itself, as that tag predates the Dockerfile, so release images start with beta.32.) -
SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft
SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft
A flaw in SAP's Cloud SDK for Python can send an application's OAuth2 client credentials to a server an attacker controls, SAP said in a security advisory on October 13. The flaw affects multi-tenant ... Read more
Published Date: Oct 13, 2026 (15 hours, 32 minutes ago)Vulnerabilities has been mentioned in this article.
CVE-2026-89111 -
💬 @rmdes — PR #960 : build: official container image with release and manual preview channels
Commentaire de pull request · PR #960 build: official container image with release and manual preview channels · @rmdes
Thanks for merging! No image has been published yet, since
docker-releaseonly runs on a published release and beta.31 came out before the merge. Could you start the workflow by hand forv1.0.0-beta.31, or would you rather wait for beta.32? Once theindiekitpackage exists, it’ll need setting to public in its package settings (org admin) fordocker pull ghcr.io/getindiekit/indiekit:betato work for everyone; the quickstart is waiting on that tag. -
Hackers force French supermarket fridges to heat up to 50C in ‘unprecedented’ cyber-attack
submitted by alyaza to news
36 points | 13 comments
https://www.theguardian.com/world/2026/oct/12/cyber-attack-defrosts-refrigerators-france-supermarket-chains-intermarche-cooperative-uHackers have forced the temperature of many French supermarket fridges up to 50C overnight, in an “unprecedented” cyber-attack affecting several hundred stores across the country, with fires and food losses reported.
The Paris prosecutor’s office said on Monday the large-scale attack was “affecting connected refrigerators in several major food retailers across France”. Reported damage included “food losses and fires”, it added.
The prime minister, Sébastien Lecornu, instructed France’s national cybersecurity agency ANSSI to investigate, a person in his office said.
France “was coordinating with its European counterparts, as other countries may also be affected”, while also investigating whether any other French firms were at risk, they said.
-
The people holding up the internet
submitted by alyaza to technology
27 points | 1 comments
https://sheets.works/data-viz/holding-up-the-internet/read -
🟢 PR #1018 — fix(indiekit): send the token to introspect in the request body
Pull request (OPEN) · PR #1018 fix(indiekit): send the token to introspect in the request body · @rmdes
Fixes #1017
introspectTokensends the token as a form-encodedtokenparameter in the POST body (RFC 7662 §2.1) instead of in the URL. TheAuthorizationheader is unchanged.The introspection mocks now match that request (no query string, token in the body), so the existing
introspectTokentests fail onmainwithMock dispatch not matched for path '/introspect?token=JWT'. An endpoint-auth test covers the other side: a token sent only in the body is accepted. -
🐛 Issue #1017 — Access tokens are sent in the introspection URL, so they end up in access logs
Issue ouverte · Issue #1017 Access tokens are sent in the introspection URL, so they end up in access logs · @rmdes
introspectTokeninpackages/indiekit/lib/token.jssends the token being checked in the URL as well as in theAuthorizationheader:introspectionUrl.searchParams.append(“token”, bearerToken);
The introspection endpoint never reads it from there (it reads
request.body.token, then the header), so the URL copy does nothing but leak a long-lived access token into access logs, and into any proxy or external IndieAuth server’s logs on the way. On a deployment every Micropub request without a session leaves a line like:POST /auth/introspect?token=eyJhbGciOiJIUzI1NiIs… HTTP/1.1RFC 7662 §2.1 has the client send the token as a form-encoded
tokenparameter in the POST body.Related to #1006.
-
Smartphone shipments dropped by 20%, lowest point in 14 years amid memory crisis
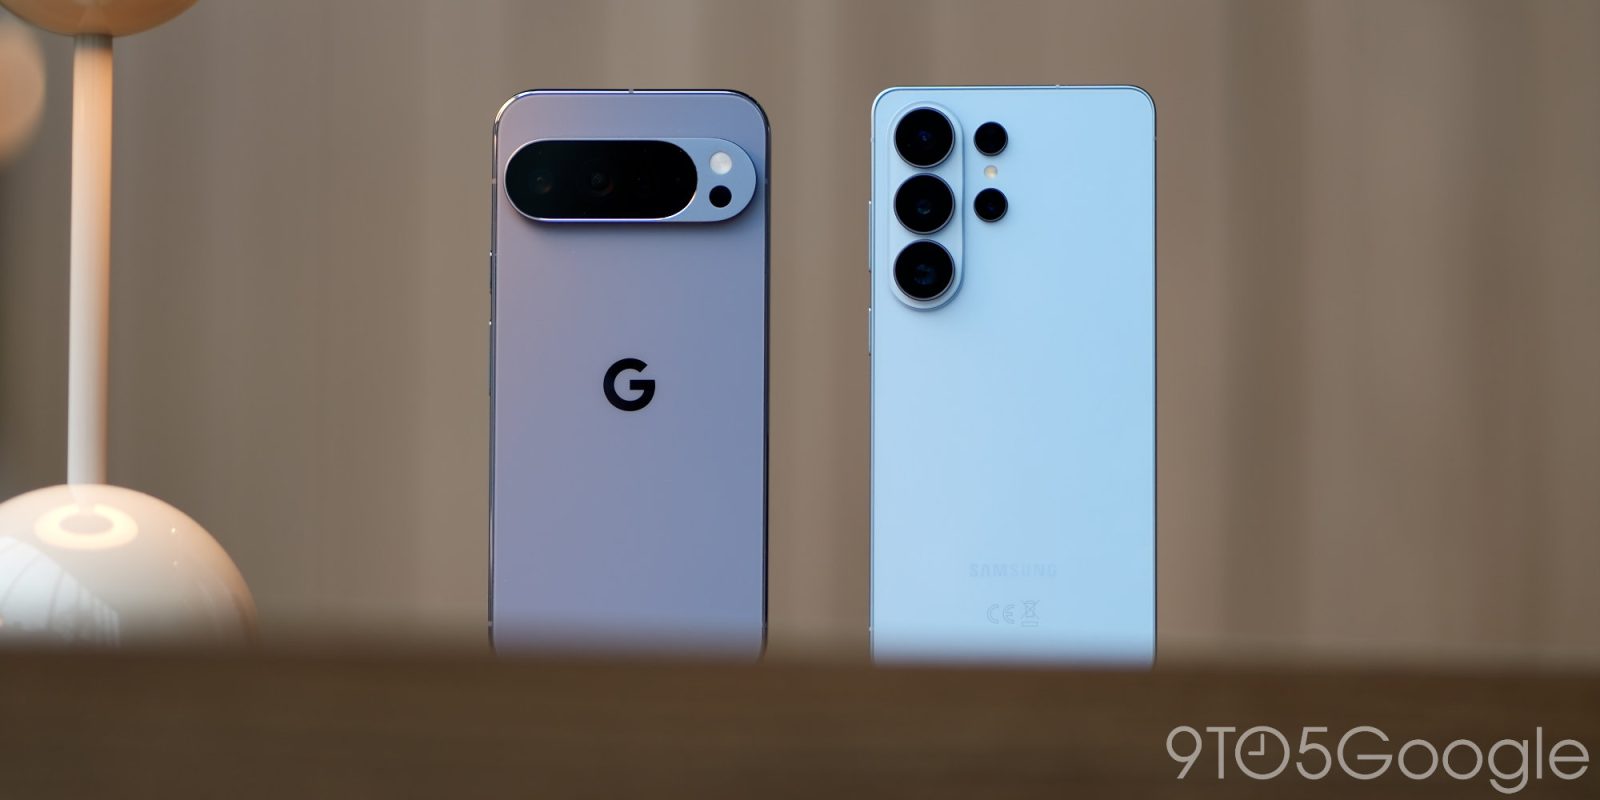
RAMageddon continues to have wide effects throughout the tech industry, with a new report revealing that the smartphone market has just hit its lowest point in well over a decade.
more… -
YouTube’s contextual AI search rolls out to all users on Android and iOS in US
“Ask YouTube” is no longer a YouTube Premium feature as the conversational AI search becomes available on mobile Android and iOS devices.
more… -
Coris (YC S22) Is Hiring Back End Engineer
Article URL: https://www.ycombinator.com/companies/coris/jobs/h0nDly8-backend-engineer-ai-native-risk-infrastructure-integrations
Comments URL: https://news.ycombinator.com/item?id=50074969
Points: 0
# Comments: 0
-
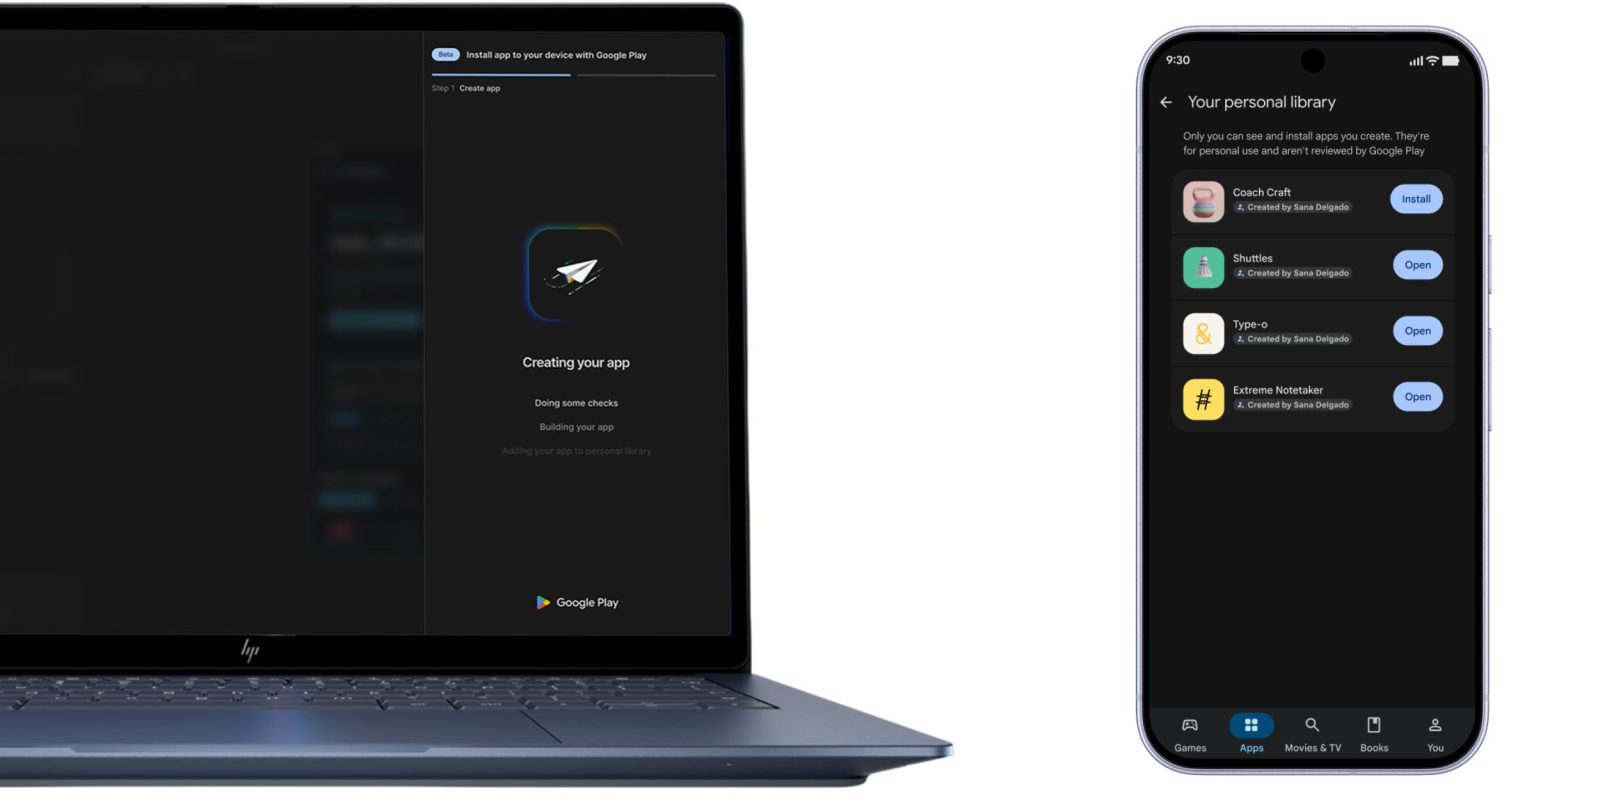
Google Play adding ‘personal library’ to access your vibe-coded Android apps
-
Show HN: How random are you?
Article URL: https://lab.specr.net/rigged-draw/
Comments URL: https://news.ycombinator.com/item?id=50074909
Points: 150
# Comments: 77
-
Gemini 4 Argon for Robotics
Main thread: Gemini 4 Argon - https://news.ycombinator.com/item?id=50073879
Comments URL: https://news.ycombinator.com/item?id=50074869
Points: 174
# Comments: 41
-
Nothing’s CMF launches new wireless speakers that look like milk cartons
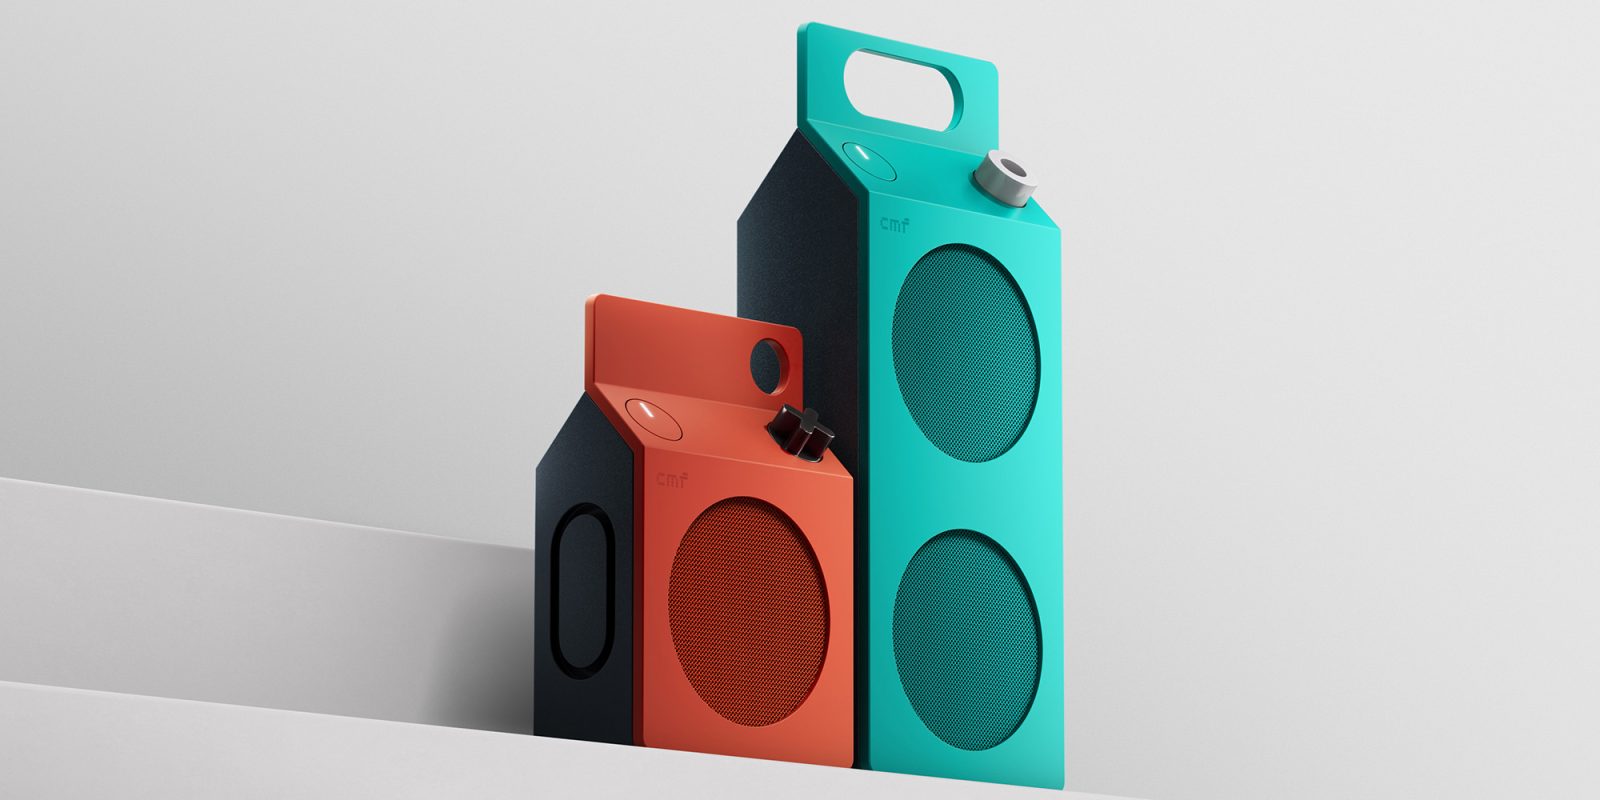
Nothing’s CMF brand has launched new wireless speakers, the first in the lineup, and they look like milk cartons.
more… -
Isocast, OBS Rewrite in Rust
Article URL: https://twitter.com/ryanvogel/status/2110047677866017087
Comments URL: https://news.ycombinator.com/item?id=50074687
Points: 1
# Comments: 0
-
Jury Convicts Ohio Blogger Of Harassment For Sending A Naked Shrek Pic To A Local Politician
In today’s episode of “wtf,” we have a jury deciding a local blogger is a criminal because a local politician didn’t appreciate being sent a Shrek bereft of clothes to his cell phone. Morgan Trau of the Ohio Capital Journal has the (pathetic) details on this particular miscarriage of justice. An Ohio political blogger let […] -
Cyberattack halts construction of tunnel between Denmark and Germany
Article URL: https://ua.news/en/world/kiberataka-zupinila-budivnitstvo-tuneliu-mizh-daniieiu-ta-nimechchinoiu-rmf24
Comments URL: https://news.ycombinator.com/item?id=50074289
Points: 130
# Comments: 108
-
Google Antigravity is now built into Gemini app for macOS
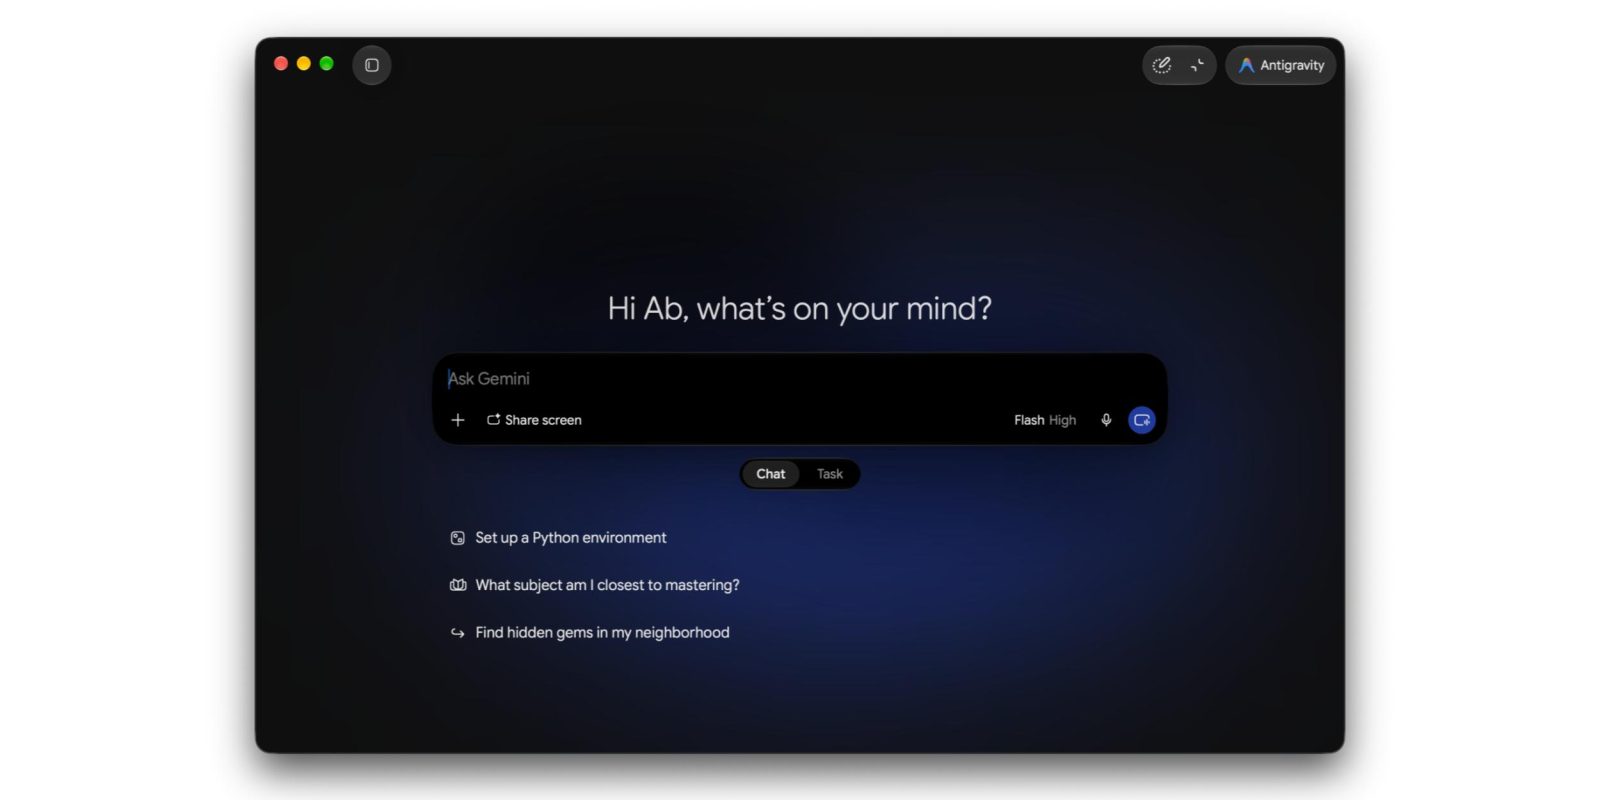
As part of today’s Gemini 4 Argon rollout, Google is making a big update to the Gemini app for macOS by integrating Antigravity.
more… -
Today we are rolling out Gemini 4 Argon globally (API, App, Antigravity)
Article URL: https://twitter.com/OfficialLoganK/status/2110038940841545827
Comments URL: https://news.ycombinator.com/item?id=50073947
Points: 1
# Comments: 1
-
Gemini 4 Argon
See also: Gemini 4 Argon for Robotics - https://news.ycombinator.com/item?id=50074869
Comments URL: https://news.ycombinator.com/item?id=50073879
Points: 1310
# Comments: 911
-
Gemini app rolling out Gemini 4 Argon to AI Pro and AI Ultra
Following the announcement at the end of September, Gemini 4 Argon is starting to roll out to the Gemini app, Google Antigravity, and more.
more… -
Redesigning source control at Anthropic
Article URL: https://www.anthropic.com/engineering/redesigning-source-control
Comments URL: https://news.ycombinator.com/item?id=50073633
Points: 775
# Comments: 786
-
Deals: Nothing Phone (3) $280 off, Headphone (a) 40% off, Pixel 11 devices up to $365 off, Lenovo Idea Tab $142, more
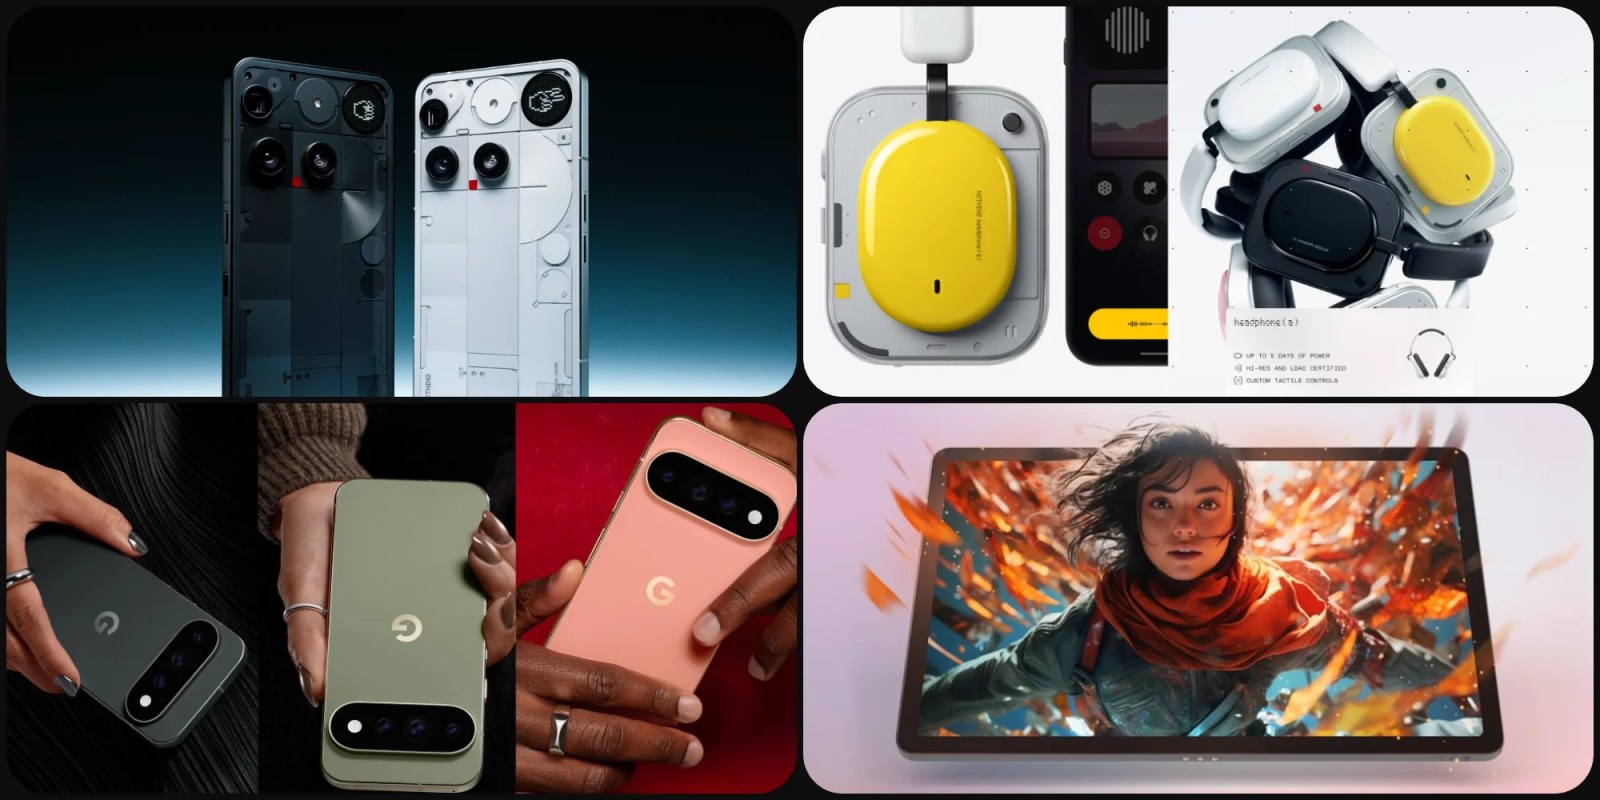
Today’s 9to5Toys Lunch Break is headlined by Nothing Phone (3) at up to $280 off its original price alongside its 2026 Headphone (a) at one of the lowest prices ever (40% off). We also have Google Pixel 11 deals back today at up to $365 off the lists, Lenovo’s budget-friendly 11-inch 2.5K Android Idea Tab at the $142 all-time low, and Anker’s new Nano Neo 45W/60W dynamic charger at just $20. Head below for a closer look at the details.
more… -
Launch HN: Consus (YC F24) – LLM gateway for companies handling sensitive data
Hey Hacker News! I'm Eric, the founder of Consus. We route all AI requests to ITAR restricted and controlled unclassified information (CUI) compliant infrastructure. Consus itself satisfies ITAR restrictions, and we recently completed our FedRAMP equivalency audit against the 410 FedRAMP High controls. FedRAMP High is the U.S. government’s strictest security baseline for cloud services handling sensitive unclassified data. A breach of this data could cause severe or catastrophic harm. Achieving FedRAMP equivalency, or authorization, is required before processing CUI information.
Demo: https://youtu.be/6MYxJe6P4oY
Aerospace and defense is experiencing rapid growth. Unfortunately, most companies are struggling to use AI because of necessary data protections & compliance risk. These companies can move even faster if they could use the AI tools that most other industries take for granted.
I spent most of my career prior to Consus in aerospace & defense. I launched national security payloads at SpaceX, and was an early employee at Castelion. I’ve watched first hand how compliance red-tape makes it difficult for companies to adopt new technologies and trust vendors that touch their sensitive data. For example, I worked with a satellite manufacturer that doesn’t allow any AI tools, even for non-sensitive work.
Even as AI has become extremely useful over the past 9-12 months, I was surprised by how many aerospace & defense companies refused to touch it. They could see how it could be helpful, but they were scared about model providers training on their data, violating an ITAR rule, or risk losing new business because of a failed cyber assessment. These are all rational fears.
There were a lot of ways to solve some/all of these problems, but we focused on building a compliant AI inference layer that can "plug" into any AI tool or workflow. Just as OpenRouter integrates with most tools, Consus can connect to tools like ChatGPT or Claude, open source tools including the Pi coding agent or Open WebUI, or integrate with applications built and maintained by individual organizations.
Almost no aerospace & defense company lives in all three major GovClouds (AWS, Azure, Google). When I mapped where frontier models can legally run for ITAR and CUI work, each provider had some subset of models, and each model achieved varying levels of compliance. Our customers don’t think in terms of cloud providers. They think about the data controls they require, and the model they want to use. That is why we built the compliance suffix. Under the hood, every request hits a single OpenAI-compatible endpoint, where keys are verified and policy is enforced before anything touches inference. Every model name must carry a compliance suffix, such as gpt-5.6-sol:fedramp-high or claude-opus-5-5:itar, and any bare model name is rejected. We never proxy to the standard commercial endpoints.
Our customers are also able to build an allowlist of models, and assign spend & model restrictions to individual users in the organization. This is all handled through our Consus Portal where teams can manage spend, keys, and policies.
A typical question we hear is why not just use Bedrock in AWS GovCloud or Azure Government directly. For small teams, just getting access to these platforms is difficult. For larger organizations, GovCloud lets you inherit some but not all of the controls needed to handle sensitive data. Also, models are split across providers: GPT-5.6 Sol is only available in Azure Government, while Claude Opus 5.5 is served through Bedrock in AWS GovCloud. If you want both, you are standing up and securing two separate government cloud environments. We run all of them behind one endpoint so customers don’t have to pick a cloud, and we handle the compliance work for each one.
Given the data sensitivities, Consus does not store any customer data at rest. All prompts and completions stay in memory only for the length of the request and are never logged or written to disk. Zero data retention is strictly enforced both on ourselves and the infrastructure/model providers. We do keep metadata on each request and response for billing and audit purposes.
Consus is not self-serve by design. ITAR requires us to know exactly who is on the other end of every key, so we verify every organization and put a contract in place before issuing API keys. We charge our customers a compliance fee starting at $40/mo/seat plus AI tokens at cost.
We are actively serving customers, and would love any feedback from security experts, or developers/engineers working in highly regulated industries!
References: API Documentation: https://gateway.consus.io/overview Security & Architecture: https://gateway.consus.io/security Compliance Details: https://consus.io/compliance
Comments URL: https://news.ycombinator.com/item?id=50073471
Points: 29
# Comments: 15
-
Now That Information Is Free, What's a College Campus For?
Article URL: https://commonedge.org/now-that-information-is-free-whats-a-college-campus-for/
Comments URL: https://news.ycombinator.com/item?id=50073455
Points: 10
# Comments: 10
-
Googlebook will improve support for Linux apps eventually, but it’s all about AI for now
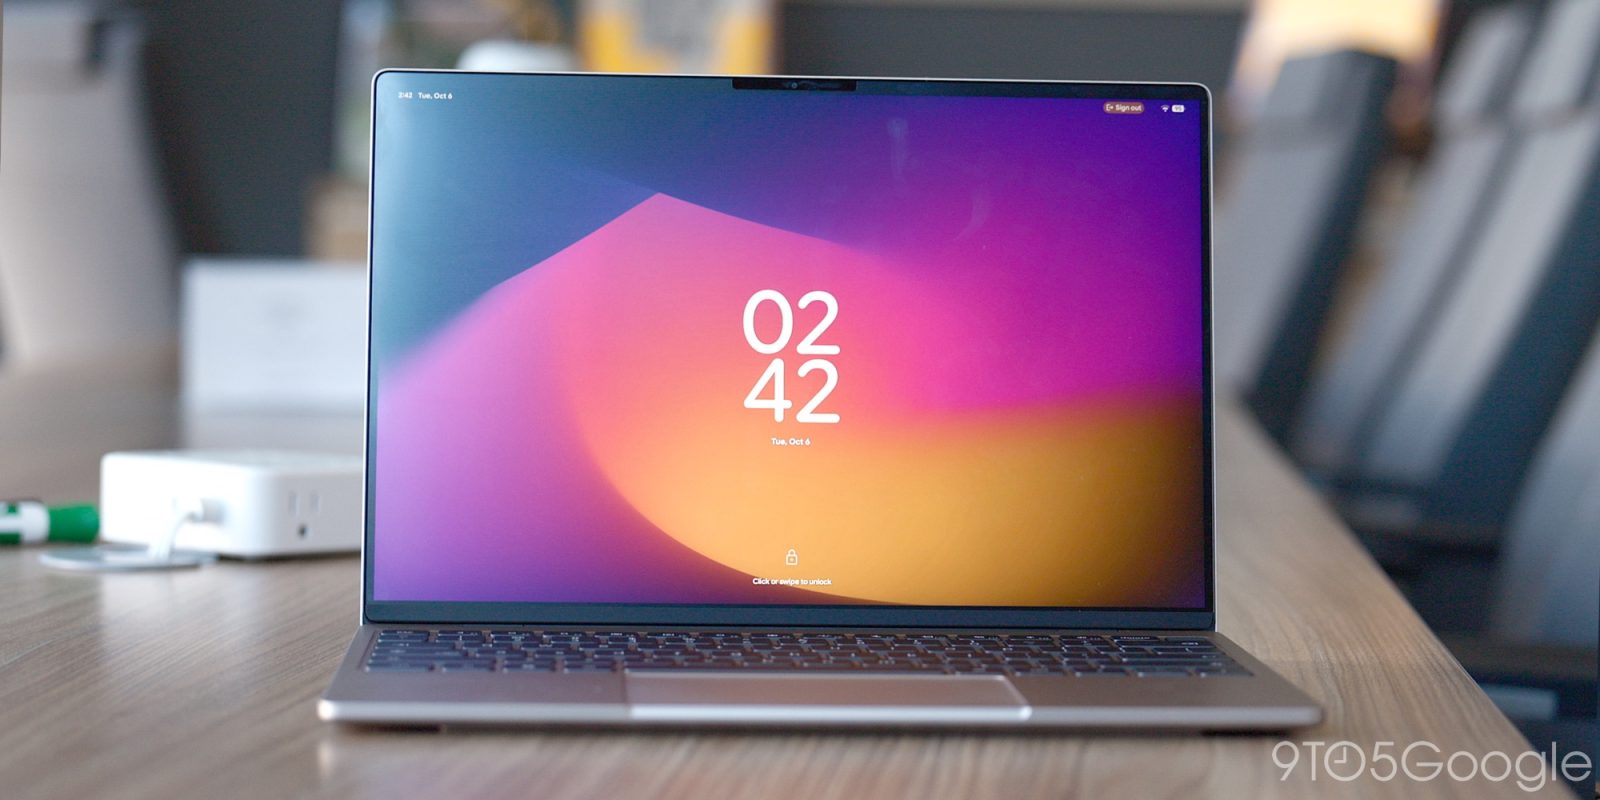
Googlebook was always going to run into problems with app availability, but few expected the platform to regress its support for Linux apps from Chromebook’s fairly robust solution. In a blog post, Google reiterates that the “Linux Terminal Preview” on Googlebook isn’t for using Linux apps, but for building with AI.
more… -
Look, just fucking use Mastodon
Article URL: https://giants-club.net/articles/just-use-mastodon/
Comments URL: https://news.ycombinator.com/item?id=50073232
Points: 8
# Comments: 3
-
I posted to HN, and then my website was flooded with AI bot traffic
Article URL: https://www.sammystraus.com/#i-posted-to-hn-and-then-my-website-was-flooded-with-ai-bot-traffic
Comments URL: https://news.ycombinator.com/item?id=50073221
Points: 313
# Comments: 170
-
Don't Run the Race – Grow
Article URL: https://alokda.wordpress.com/2026/10/13/dont-run-the-race-grow/
Comments URL: https://news.ycombinator.com/item?id=50073171
Points: 1
# Comments: 0
-
Samsung’s first Android XR glasses leak in 25 styles alongside 9-hour battery, specs [Gallery]
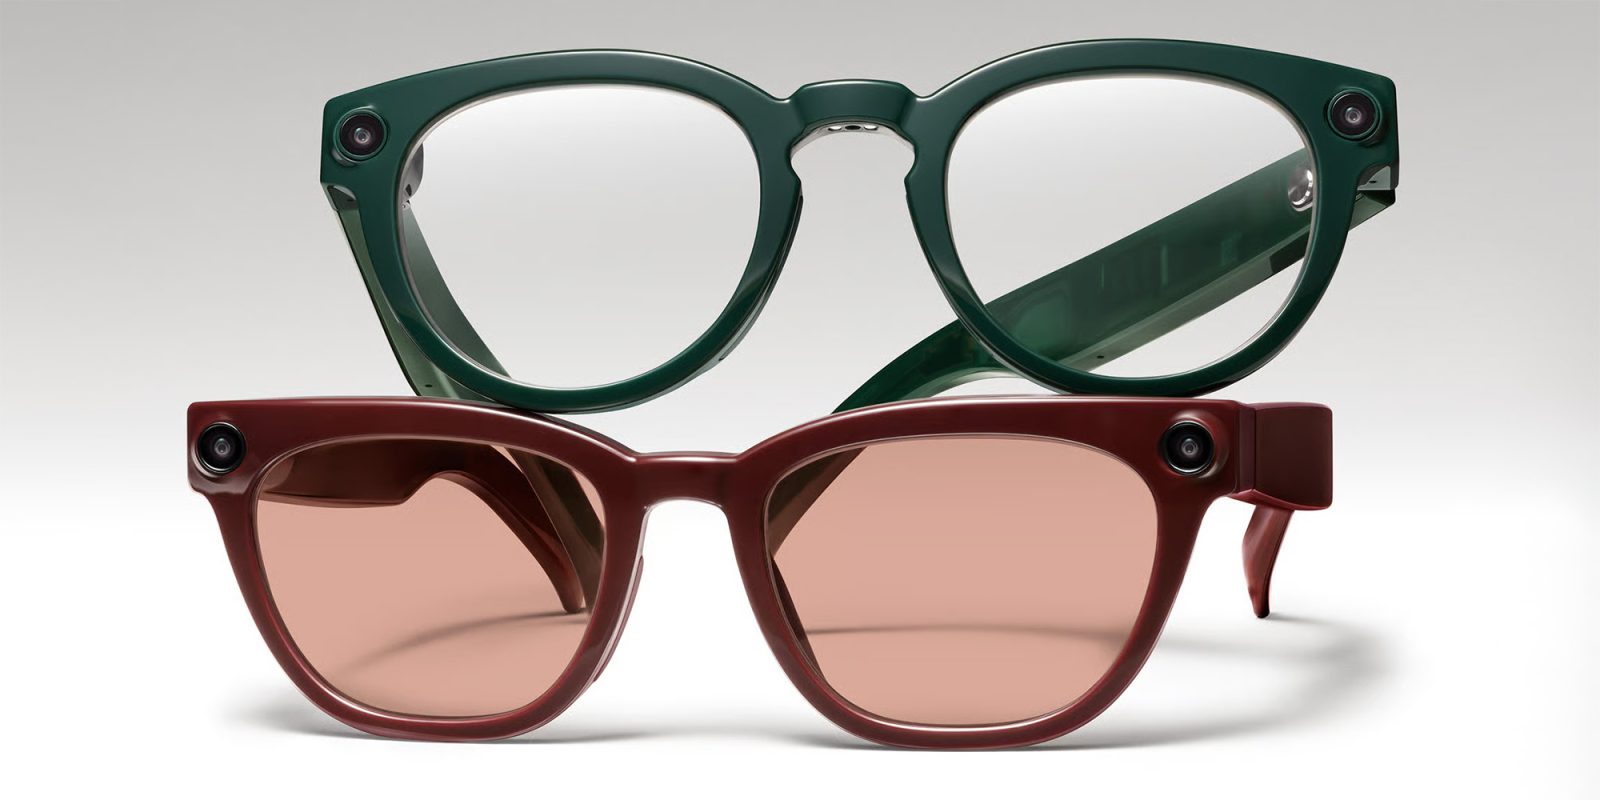
Samsung’s first Android XR glasses are right around the corner and, ahead of launch, another leak reveals every style you’ll be able to buy.
more… -
The United Kingdom generates less electricity per person than in the 1970s
-
Thunderbird for iOS
Article URL: https://blog.thunderbird.net/2026/10/thunderbird-for-ios-a-first-look-at-the-native-iphone-email-app-in-development/
Comments URL: https://news.ycombinator.com/item?id=50072913
Points: 439
# Comments: 187
-
Ivanti waarschuwt voor misbruik van lek in Connect Secure vpn-servers
Ivanti waarschuwt voor misbruik van lek in Connect Secure vpn-servers
Ivanti waarschuwt klanten voor actief misbruik van een kwetsbaarheid in Ivanti Connect Secure vpn-servers. Via het beveiligingslek (CVE-2026-104935) kan een ongeauthenticeerde aanvaller willekeurige c ... Read more
Published Date: Oct 13, 2026 (18 hours ago)Vulnerabilities has been mentioned in this article.
CVE-2026-104935 -
Import Twitter Data Archive Using WP-CLI Resources
Article URL: https://github.com/shawnhooper/twitter-archive-to-wp
Comments URL: https://news.ycombinator.com/item?id=50072430
Points: 1
# Comments: 0
-
Here’s the full list of OnePlus devices getting Android 17, but it’s not OxygenOS
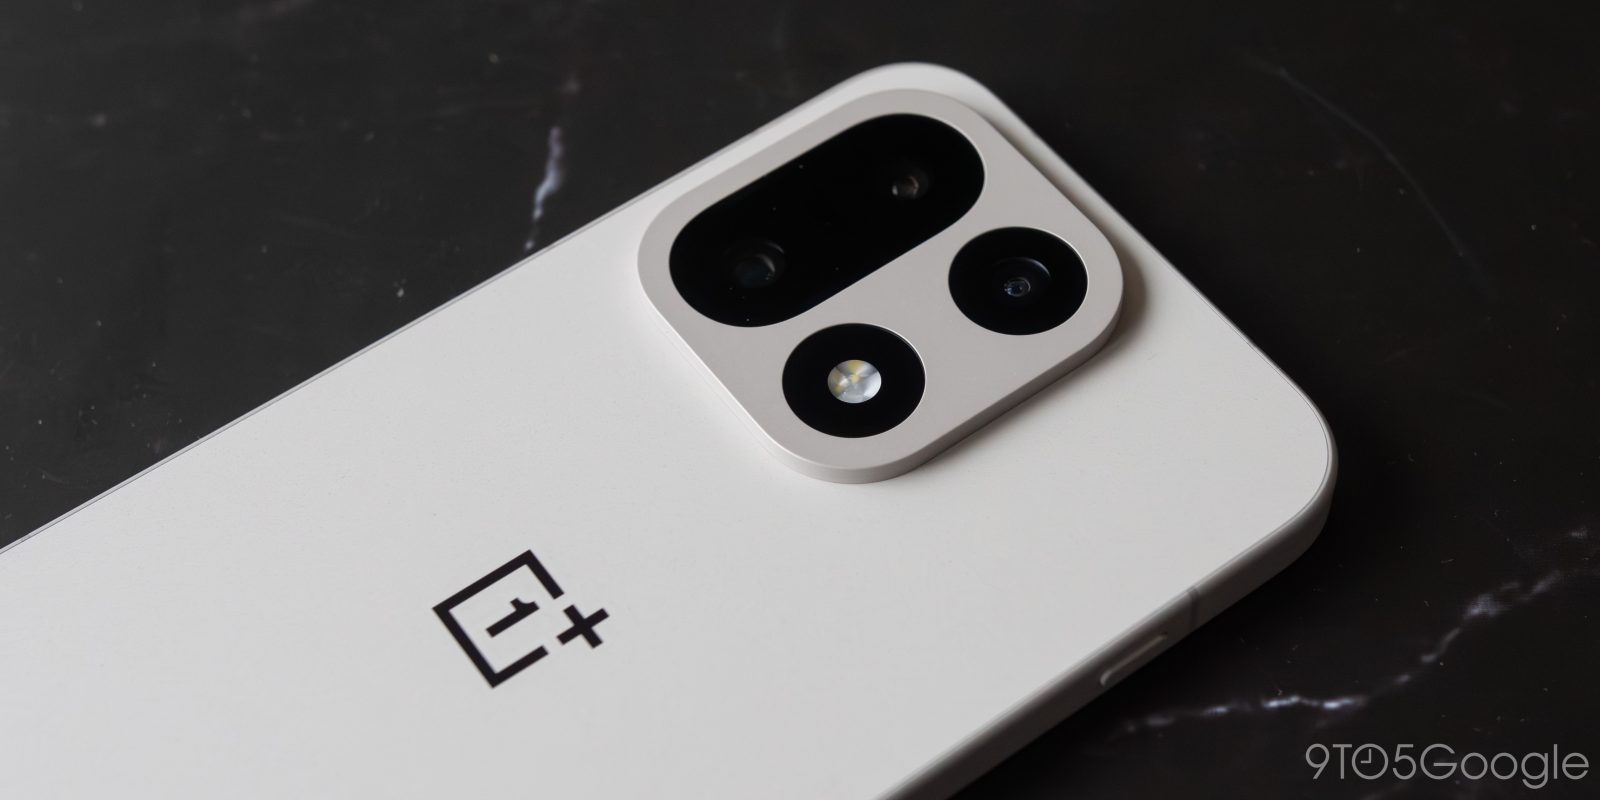
OxygenOS, the flavor of Android for OnePlus devices, is officially going away as the brand steps out of the global market, with Oppo’s ColorOS taking over starting with Android 17. And, now, we have an official list of OnePlus devices getting Android 17 starting later this month.
more… -
Apple's new 'Switch to Safari' campaign details why you should ditch Chrome
https://www.apple.com/safari/switch/
Comments URL: https://news.ycombinator.com/item?id=50072286
Points: 273
# Comments: 474
-
A Book That Will Never Be Read
Article URL: https://forbetterscience.com/2026/09/22/a-book-that-will-never-be-read/
Comments URL: https://news.ycombinator.com/item?id=50072229
Points: 30
# Comments: 10
-
Oppo confirms list of devices getting its Android 17 update, rollout starts this month
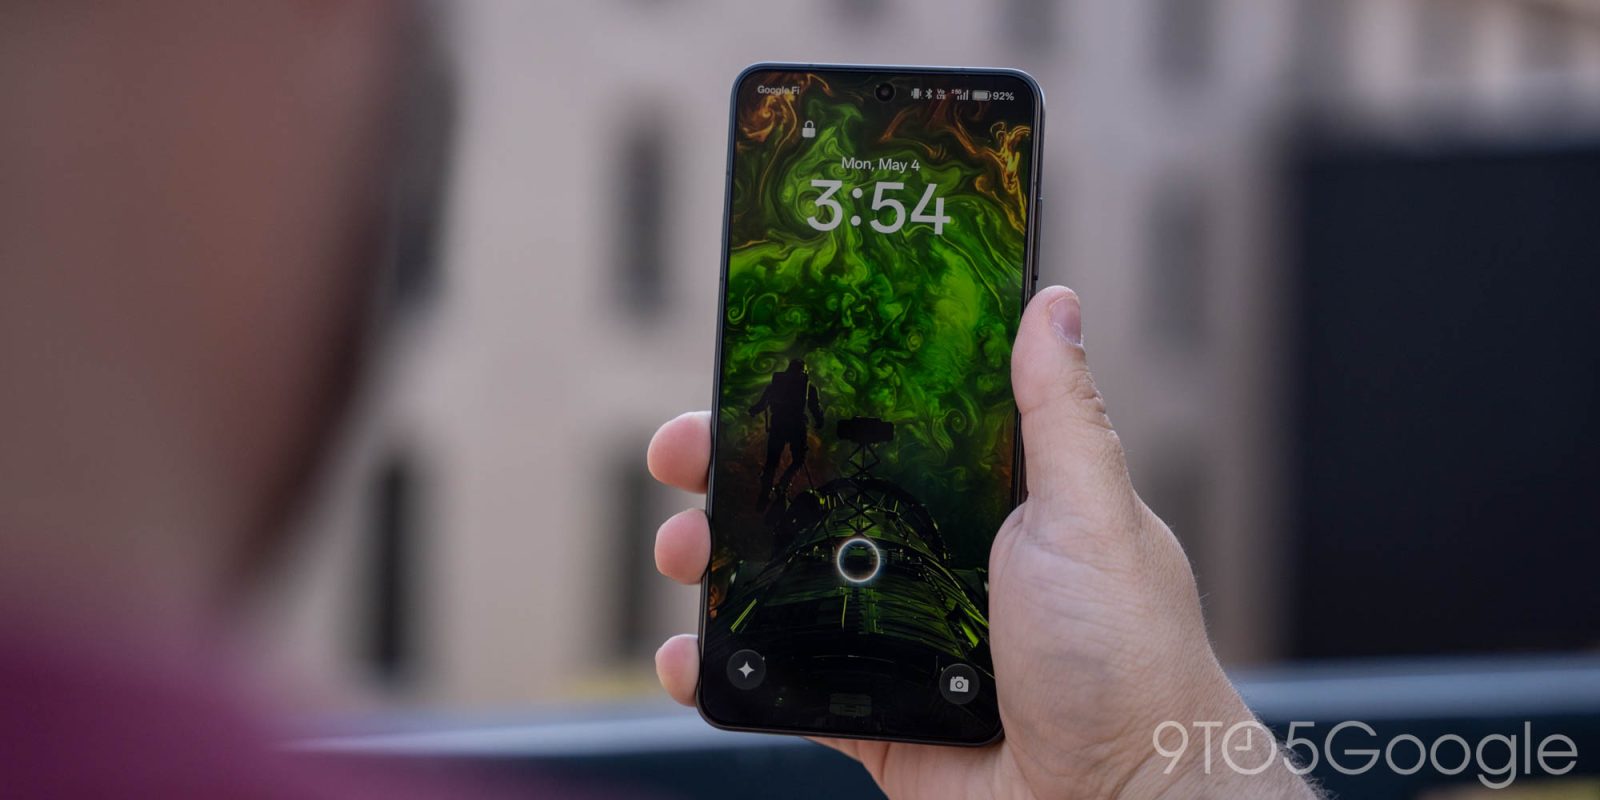
Oppo has officially revealed ColorOS 17, its Android 17 update, to global markets this week and, along with that, confirmed a list of devices poised to get the update.
more… -
How to engineer an AI harness for game development
Article URL: https://kylekukshtel.com/ai-harness-engineering-game-development-claude-code
Comments URL: https://news.ycombinator.com/item?id=50072120
Points: 149
# Comments: 73
-
OpenAI Fires Three Safety Researchers
Article URL: https://thezvi.wordpress.com/2026/10/12/openai-fires-three-safety-researchers/
Comments URL: https://news.ycombinator.com/item?id=50071533
Points: 3
# Comments: 1
-
Same Job, Two Engines: InnoDB and Iceberg Internals
Article URL: https://marcpaul.io/logs/same-job-two-engines-innodb-and-iceberg-internals/
Comments URL: https://news.ycombinator.com/item?id=50071466
Points: 9
# Comments: 0
-
Trying Out the New VBCC-65816 Compiler
Article URL: https://bumbershootsoft.wordpress.com/2026/10/10/trying-out-the-new-vbcc-65816-compiler/
Comments URL: https://news.ycombinator.com/item?id=50071326
Points: 1
# Comments: 0
-
Zxloader.system: a compressed binary loader for Apple II
Article URL: https://www.colino.net/wordpress/archives/2026/10/10/zxloader-system-a-compressed-binary-loader-for-apple-ii/
Comments URL: https://news.ycombinator.com/item?id=50071312
Points: 1
# Comments: 0
-
New Apple TV 4K
Article URL: https://www.apple.com/newsroom/2026/10/apple-unveils-the-new-apple-tv-4k/
Comments URL: https://news.ycombinator.com/item?id=50071310
Points: 297
# Comments: 557
-
Show HN: Stream live open data in two commands
A service and open source tool to get open data streams in two commands. No sign up needed for subscribing.
Streams to try:
- https://hypermass.io/stream/_J0fm450s - extreme UV images of the sun from SOHO - visual data
- https://hypermass.io/stream/_ATtCoEK - GDACS live disaster data (filtered to just the ongoing items)
The CLI (Apache 2.0, https://github.com/hypermass-io/hypermass-cli) tool allows you to subscribe to multiple live streams of files, with the files arriving in a local folder. The filenames are ULIDs so they can be easily sorted into time order in scripts and code. Publishing works similarly - drop files into a folder and they get read, published and deleted locally. The idea is that by being highly opinionated about the shape of the data (files, delivered in sequence, in real time) a bunch of the logic and edge cases get handled well in one place (things like ordering, retries, hash verification, reconnection, etc) - rather than requiring every subscriber to implement it themselves for every source.
A high-speed version for things like departure boards, train positions is in the pipeline.
Background: About 10 years ago, I worked for a few years supporting and developing some of the UK Rail Open Data systems. As a developer I was frustrated at how fragmented the open data space was, and how every open data system was designed as a blank-page exercise. I realised that a lot of data falls into an odd middle ground, too infrequent to economically poll on a large scale, too large for messaging protocols, but in some sense still real time. For example transport schedules, periodic solar imagery, disaster alerts - real-time but infrequent.
Fairly often I just wanted a "just give me the data" option when the solutions I found were static catalogues with no nod towards real-time use, bespoke APIs, analytics systems and other things I didn't need. I couldn't find a simple approach that leaned into what I saw as the data's strengths (simple files, delivered in order, as/when they are published) - so I built it.
About me: Solo founder based in the UK, full time for just over a year.
Sustainability: Initially a "heavy users pay for more data allowance" model with a decent free tier. Ideally we later shift to institutional publishers pay to keep their streams free to download. Possibly a paid data marketplace to support costs, but the main focus would always be the free and open data.
What I'd like to know:
- Does the CLI approach solve any real problems for you?
- Is the technical approach sane?
- Would you use a service like this to publish data?
- Recommendations to bootstrap users (particularly publishers)?
Comments URL: https://news.ycombinator.com/item?id=50071200
Points: 6
# Comments: 1
-
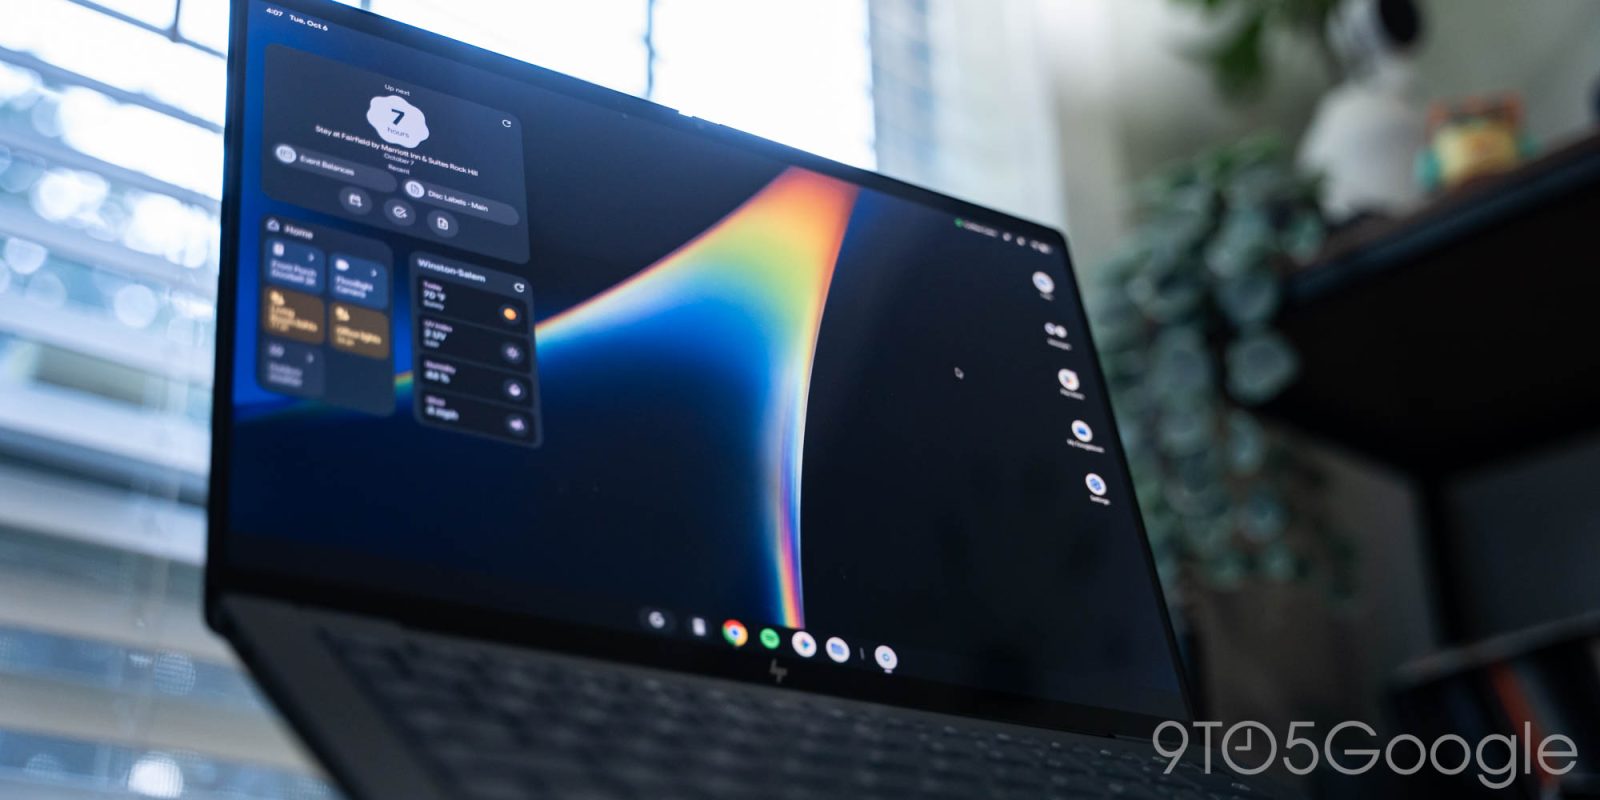
If a Chromebook wasn’t for you, Googlebook isn’t either
-
Apple HomeView
Article URL: https://www.apple.com/apple-homeview/
Comments URL: https://news.ycombinator.com/item?id=50071017
Points: 730
# Comments: 854
-
Marc Andreessen reveals why housing, health care, and edu getting more expensive
Article URL: https://twitter.com/jaynitx/status/2109957970591412722
Comments URL: https://news.ycombinator.com/item?id=50070770
Points: 2
# Comments: 3
-
BB(10) > Graham's Number